
Our cookie consent rate was 2.75%, so we saw real data on about 3% of visitors. What GDPR, POPIA and US law require, what Consent Mode can't fix, and why we kept the banner.
Honestly, few things have changed web analytics as dramatically (and as annoyingly) as the rise of the cookie consent banner. What started as a polite "we use cookies" notice has mutated into a full-screen legal pop-up that half the internet now ignores.
For the past few months, we've been running Enzuzo as our Consent Management Platform (CMP) here at Milk Moon Studio.
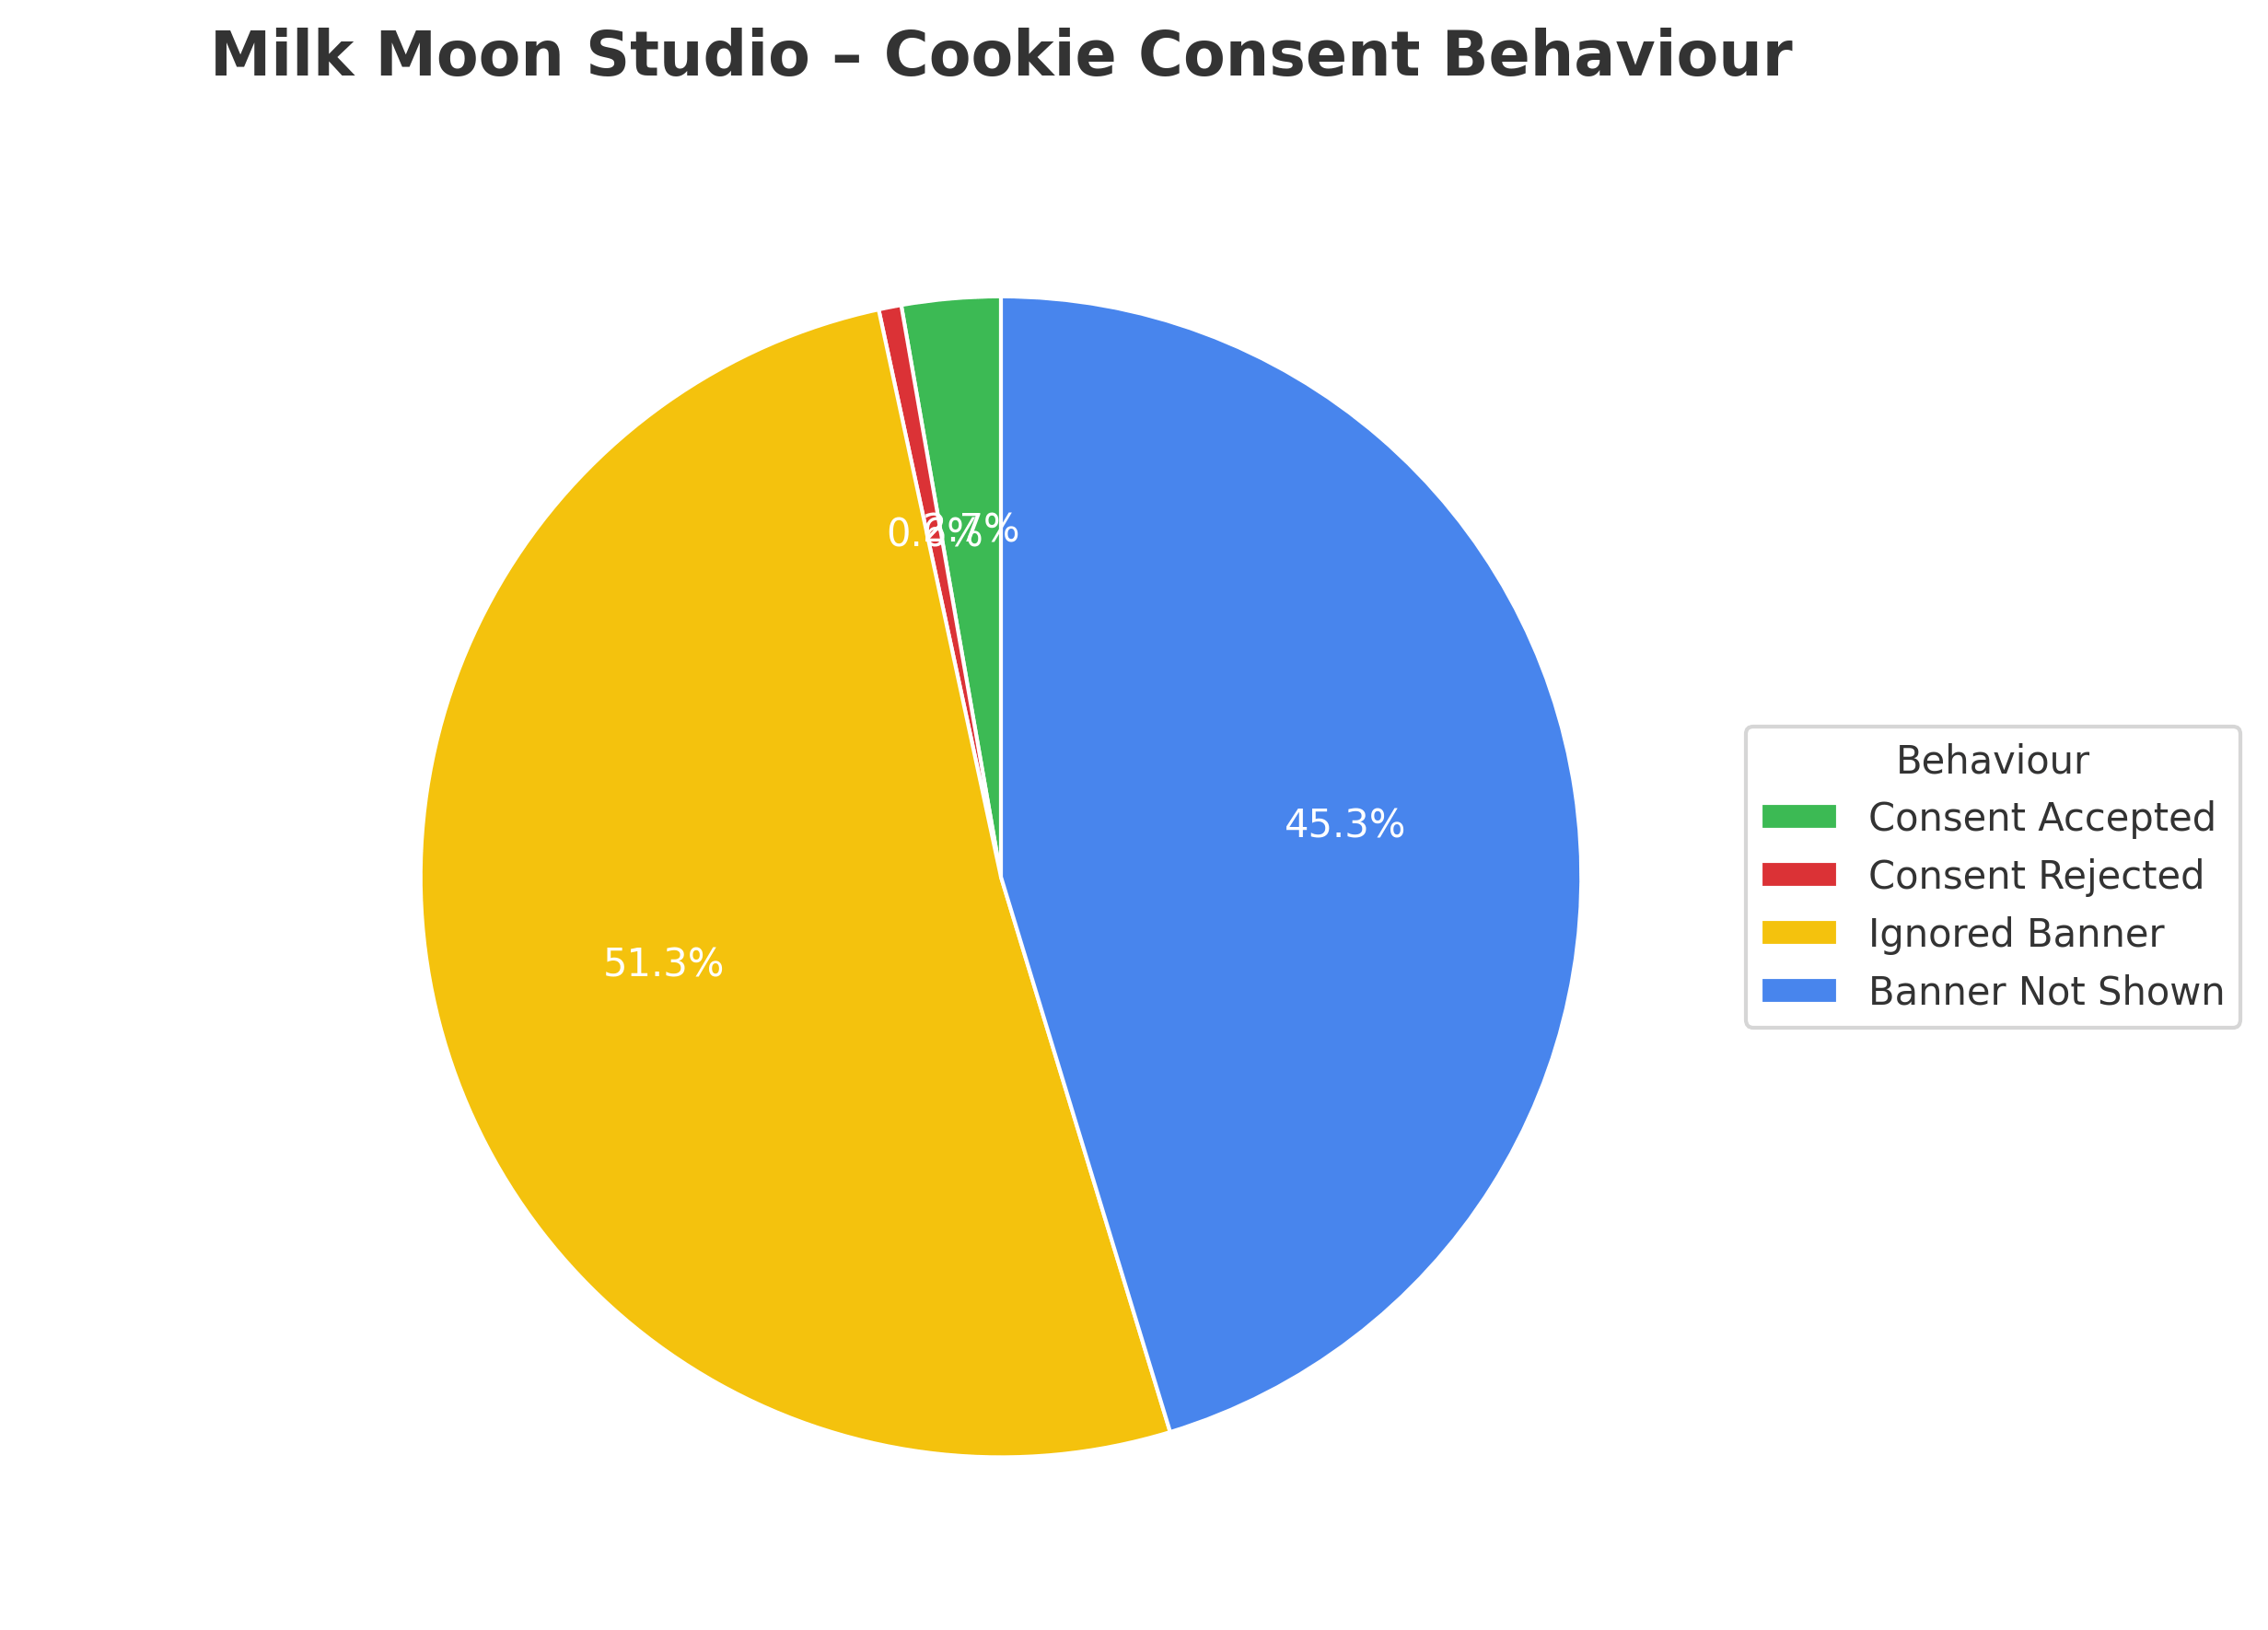
The numbers are... brutal. Out of every hundred visitors, fewer than three actually click Accept. That's a 2.75% cookie consent rate, less than the margin of error in most surveys. Another 0.63% hit Reject, over half (51%) just stare blankly and do nothing, and 45% never see the banner at all thanks to blockers or geo-logic.
In other words, we're collecting fully compliant, high-fidelity analytics data on maybe three percent of our audience.
Everyone else is invisible.
This got us thinking (and researching, and debating, and maybe losing some sleep):
What's the real cost of compliance?
Are we haemorrhaging valuable data for the sake of legal requirements? Or have cookie banners done more damage to data than privacy ever did?
If you run a Webflow site (or any site, really) with analytics, marketing tools, or even just basic cookies, you've probably had these same late-night debates: Do we really need a cookie consent banner? Should we go full CMP or keep it simple? What actually happens, both legally and practically, if you don't do it by the book?
Let's dig into the legal requirements across three major jurisdictions: the EU (GDPR), the USA, and South Africa (POPIA), examine real-world enforcement cases, compare our consent data against global trends, and figure out what the hell is actually happening to the web analytics landscape.
How we got here
The original idea was simple: give users control over how their data is used. In practice, that noble goal collided with the internet's addiction to tracking everything that moves.
GDPR arrived in 2018 and set the tone: no non-essential cookies without explicit, informed, opt-in consent. No pre-ticked boxes. No implied permission. You want to track someone? Ask first, and make it just as easy to say no.
Then came POPIA in South Africa, which borrowed much of GDPR's DNA, and the slow-burn rise of U.S. state privacy laws like CCPA/CPRA, Colorado's CPA, and Virginia's VCDPA. The details differ, but the gist is the same: people get to decide what data you collect, and you have to tell them when you're doing it.
It all sounds reasonable until you realise what happens when people are actually given a choice.
The reality check: our Enzuzo cookie consent rate vs. the industry
Before we get into the legal maze, let's look at what's actually happening on our website, and how it compares to everyone else:
Milk Moon Studio's numbers:
- Total Pageviews: 100%
- Consent Accepted: 2.75%
- Consent Rejected: 0.63%
- Ignored Banner: 51.33%
- Dismissed Banner: 0%
- Banner Not Shown: 45.29%
Let that sink in. More than half of our visitors (51.33%) completely ignore the banner. Another 45.29% never even see it (likely return visitors who've already made a choice, users with certain browser configurations, or blockers). Only 2.75% actively accept, and less than 1% actively reject.
How does this compare globally?
Here's where it gets interesting (or depressing, depending on your perspective). According to recent industry studies and CMP providers:
- EU Average (Strict Opt-In): 3-7% explicit acceptance for well-designed banners, with some sites hitting as high as 15% when users really trust the brand
- Rejection Rates: When users are presented with a clear "Accept" or "Reject" option (as required by GDPR), rejection rates typically range from 50-60% or even higher
- US Average: 10-20% acceptance (higher because many sites use implied consent or less aggressive blocking)
- Global Average: 5-10% explicit acceptance
- Ignore Rate: Industry-wide, 40-60% of users simply don't interact with cookie banners at all
Update, October 2026: A word on how these numbers get measured, because it matters more than we realised. A "consent rate" can mean the people who hit Accept all, or anyone who gave any consent at all (including picking a category or two in the settings), and it can be counted per visitor, per session or, like Enzuzo does it, per pageview. Our 2.75% is Accept clicks against every pageview, including the 45% where the banner never showed. Count only the pageviews that actually showed it and we're closer to 5%. That's why published studies are all over the place. The biggest one we found, Advance Metrics' cookie behaviour study (a five-year follow-up to their original 2018 study of more than 1.2 million users), looked at international B2B websites in the first half of 2023 and found 25.4% of users accepted all cookies straight off the banner, while only 33.6% ignored it. So take the ranges above as rough, and some sites clearly do a lot better than we do. The point still stands, though: most people ignore the banner or say no, and even at 25% you're flying three-quarters blind.
What does this tell us?
Our 2.75% acceptance rate is low, but not wildly out of range for a strict opt-in implementation. We're actually on par with (or maybe slightly below) the EU average. So our Enzuzo stats are bad, but they're also perfectly normal. Everyone is flying blind together.
This isn't an "us" problem. This is an industry-wide shift in how web analytics works.
The great analytics blackout: what this means for data quality
Here's the brutal maths: If we're being fully compliant with GDPR and POPIA, we're working with accurate data on less than 3% of our traffic from EU and South African visitors.
That blindness has consequences. With 97% of visitors untracked, your conversion rates are fake, your funnels are broken, and your "audience insights" are more like horoscope readings than hard data.
The implications are staggering:
- Massively incomplete data: We're missing data on 97%+ of visitors
- Wildly inaccurate metrics: Conversion rates, bounce rates, time on site, traffic sources: everything is skewed
- Useless for decision-making: You can't make informed business decisions based on data from 3% of your audience
- Biased sample: The 2.75% who consent aren't a random sample. They're a specific subset of users who may be more engaged, more trusting, or from different demographics
- Underreporting conversions: Your actual conversions might be much higher than what Analytics shows
- Misallocation of resources: You might overinvest in channels that produce higher consent rates while ignoring channels with lower consent but better real ROI
For advertising, it's even worse:
For anyone running ads, the pain doubles. Without consent signals, Google Ads switches off remarketing and personalised audiences entirely. You're left shouting into the void with generic targeting, and good luck optimising campaigns when your conversions are missing half their attribution data:
- Severely limited remarketing audiences (only 2.75% can be remarketed to)
- Degraded conversion tracking (can't track which ads led to conversions if users didn't consent)
- Impaired optimisation (Google's algorithms can't optimise without consent signals from most users)
- Wasted ad spend (showing ads to people who already converted, or missing people who should see them)
And even if you bend over backwards with Google's Consent Mode v2, all you get is statistical modelling. GA4 tries to fill in the blanks with "behavioural modelling" and "conversion modelling," but that's really just fancy guessing. Better than flying completely blind, but not even close to having real data.
And a small site might not even get the guessing. GA4 only switches on behavioural modelling once a property has at least 1,000 daily users with analytics consent granted on at least 7 of the previous 28 days, plus at least 1,000 events a day from people who said no, for at least 7 days. At a 2.75% cookie consent rate you'd need somewhere north of 36,000 visitors a day to clear the first bar, so for most small business sites the modelling simply never kicks in.
Meanwhile, the regulators aren't playing: GDPR rules the EU
What the law actually says
The General Data Protection Regulation (GDPR) has been in effect since May 25, 2018, and it doesn't mess around. If you're processing personal data of anyone in the European Union, you need to comply, regardless of where your business is actually located.
Key requirements for cookie consent:
- Explicit, Informed Consent: Users must actively opt-in before you place any non-essential cookies on their device. Pre-checked boxes don't count. "Implied consent" doesn't exist under GDPR. No consent = no tracking.
- Granular Control: Users need the ability to accept or reject different categories of cookies separately (analytics, marketing, functional, etc.). You can't bundle "Accept All" as the only option.
- Clear Information: You must explain what data you're collecting, why you're collecting it, who you're sharing it with, and how long you're keeping it. The ePrivacy Directive and GDPR together mandate this transparency.
- Easy Withdrawal: Users must be able to withdraw consent as easily as they gave it. If accepting takes one click, rejecting or withdrawing should too.
- No Cookie Walls: You generally can't deny access to your website if someone rejects non-essential cookies. (There are narrow exceptions, but they're hard to justify.)
- Documented Consent: You need to maintain records proving that consent was obtained, when, and for what purposes. If someone files a complaint, you need to show proof.
- No Pre-Ticked Boxes: The landmark CJEU decision in Planet49 clarified that even for cookies, pre-ticked boxes violate the law. Consent must be an affirmative action.
- Legitimate Interest Doesn't Apply: Recent enforcement trends make it crystal clear: you can't use "legitimate interest" as a lawful basis for non-essential cookies like analytics or marketing.
What counts as personal data?
This is where it gets tricky. Google Analytics (even GA4) collects data that can be considered personal under GDPR:
- IP addresses (even when "anonymised," Google receives the full IP before truncation)
- Client IDs and User IDs
- Device identifiers
- Browsing behaviour that can create a "digital fingerprint"
European regulators (the national data protection authorities, like France's CNIL) have been crystal clear: Google Analytics requires consent. Strictly speaking, that comes from each country's cookie rules, with GDPR setting the bar for what counts as consent.
Real-world enforcement: they're not bluffing
The reason we can't just shrug and collect data anyway is that regulators have teeth, and they've used them. Let's look at some actual cases where companies got hit for cookie compliance failures:
Google vs. France (September 2025): The French data protection authority (CNIL) slapped Google with a €325 million fine for inserting ads into Gmail without proper user consent and coercing users into accepting cookies through dark patterns. It's one of the largest cookie consent fines ever handed out (technically under France's cookie rules, the ePrivacy side of the law, rather than GDPR itself).
IAB Europe (February 2022): The Belgian Data Protection Authority found IAB Europe's Transparency and Consent Framework non-compliant with GDPR, ordering major changes to how ad tech companies obtain consent. Fine: €250,000 plus orders to delete massive amounts of improperly collected data.
Google Analytics Decisions (2022-2023): Data protection authorities in Austria, France, Italy, Denmark, Finland, Norway, and Sweden all ruled that using Google Analytics violates GDPR due to data transfers to the US, even with consent. Some required websites to stop using GA entirely. (Worth knowing: those rulings were about sending data to the US before the EU-US Data Privacy Framework came into force in July 2023. Google is certified under it, so the transfer problem is parked for now. The consent requirement didn't go anywhere.)
Smaller Companies Are Getting Hit Too: It's not just tech giants. In January 2022, a Munich court ordered a website operator to pay a visitor €100 in damages for loading Google Fonts from Google's servers without consent (which sends the visitor's IP address to Google), and threatened fines of up to €250,000 if they kept doing it. French companies have been fined for cookie banners that didn't allow easy rejection.
Dark Patterns Are Being Targeted: California's Privacy Protection Agency and a new Consortium of Privacy Regulators across multiple US states are now actively targeting cookie banners that use "dark patterns": making "Accept" bright and prominent while burying "Reject" in grey text or requiring multiple clicks.
So even if enforcement is inconsistent, the pattern is clear: privacy laws aren't a phase. They're a one-way ratchet.
The stakes
GDPR violations can cost you:
- Up to €20 million OR 4% of annual global revenue, whichever is higher
- Legal fees, audit costs, and remediation expenses
- Reputational damage
- Being ordered to cease data processing entirely
- Civil claims from affected individuals
- Active complaints from privacy advocacy groups like NOYB (which actively hunts for violations)
For a small agency like ours, even a "small" GDPR fine would be business-ending.
The Google factor: when platforms become police
Here's where it gets less about the law and more about practicality.
Even if you were brave enough to ignore compliance, Google won't let you. As of March 2024, every site using Analytics or Ads in the EEA and UK (and Switzerland since July 2024) must implement Consent Mode v2.
If you don't send Google valid consent signals:
- GA4 stops collecting full data for non-consenting users
- Ads remarketing lists won't populate
- Conversion tracking goes fuzzy
- Ad personalisation shuts down
- Your campaign performance nosedives
So yes, you could remove the banner, but your analytics and ads would instantly become half-functional at best. Google has essentially become the de-facto enforcement arm of GDPR. This is enforcement you can't ignore.
Risk level for non-compliance: HIGH
Even small companies are getting caught. Users can file complaints. Privacy advocacy groups actively hunt for violations. Data Protection Authorities issue billions in fines, actively investigate cookie consent violations, respond to complaints, and coordinate cross-border enforcement.
POPIA: South Africa follows the EU's lead
What the law says
The Protection of Personal Information Act (POPIA) came into full effect on July 1, 2021, and shares many principles with GDPR. If you process the personal information of South African data subjects, POPIA applies to you.
Key requirements:
- Consent Must Be Voluntary, Specific, and Informed: Same standard as GDPR when you rely on it. Consent is one of six lawful grounds for processing in section 11 (legitimate interest is another), so POPIA doesn't demand consent for every bit of processing. For analytics and marketing cookies, though, informed, prior consent is the safe route, and it's the one we take.
- Purpose Specification: You can only collect data for explicitly defined, lawful purposes. You must communicate these purposes clearly.
- Data Minimisation: Collect only what's necessary for your stated purpose.
- Security Safeguards: You must secure personal data against unauthorised access, loss, or damage.
- Data Subject Rights: Individuals can request access to their data, request corrections, or object to processing.
- Cross-Border Transfers: POPIA regulates sending data outside South Africa, so you need safeguards when transferring data to Google's servers overseas (like Standard Contractual Clauses).
What counts as personal information under POPIA?
POPIA defines personal information broadly:
- IP addresses
- Device identifiers
- Cookies that can identify or relate to an identifiable person
- Browsing behaviour tied to an individual
Yes, Google Analytics falls under this definition. While POPIA doesn't yet provide cookie-specific regulations, legal commentary generally treats cookies as processing of personal information.
Real-world enforcement: early days but getting serious
POPIA enforcement is still ramping up compared to GDPR, but the Information Regulator (the South African DPA) is taking action.
In South Africa, enforcement is newer but warming up. The Information Regulator has started issuing multi-million-rand penalties for sloppy data handling, and the complaints are piling up:
2023, the first POPIA fine: The Department of Justice and Constitutional Development was fined ZAR 5 million for ignoring an enforcement notice after a 2021 ransomware attack (it hadn't renewed its antivirus and other security licences). Note the route: breach, then enforcement notice, then the fine when the notice was ignored.
Multiple Complaints Filed: The Information Regulator's office has reported receiving thousands of complaints, many related to digital tracking, marketing communications, and lack of consent mechanisms.
The enforcement is slower than Europe, but it's happening. And the penalties are serious.
The stakes
POPIA violations can result in:
- Fines up to ZAR 10 million (approximately $550,000 USD)
- Imprisonment for up to 10 years for specific offences, like obstructing the Information Regulator or not complying with an enforcement notice (not for the processing itself)
- Civil claims for damages
- Orders to cease processing
- Reputational damage in the South African market
For companies doing business in South Africa, POPIA compliance isn't optional. It's just a matter of time before enforcement catches up with violators.
Google's requirements
Not quite the same as GDPR, as it turns out. Google's EU user consent policy (the one behind the Consent Mode requirement) covers the EEA, the UK and Switzerland, not South Africa. But if you're running a CMP for POPIA anyway (and you should be), hook it up to Consent Mode so Google Analytics and Ads respect the choices your visitors make.
Risk level for non-compliance: MEDIUM (but increasing)
The Information Regulator has limited resources compared to EU DPAs, is prioritising egregious cases (data breaches, malicious violations), and responds to complaints but slowly. However, the risk is real and growing. If you're doing significant business in SA, don't gamble on this.
USA: the patchwork approach (or: the distracted uncle of privacy law)
Here's a helpful way to think about the jurisdictions:
Europe is the strict parent: "Ask before you touch anything."
The U.S. is the distracted uncle: "Just don't sell it and you'll probably be fine."
South Africa is the younger sibling, watching the EU's mistakes and slowly arming itself with the same rules.
Federal law: basically nothing (for now)
Unlike the EU and South Africa, the United States has no comprehensive federal privacy law. No GDPR equivalent. No POPIA equivalent.
However, there are federal laws for specific sectors:
- COPPA: Children's Online Privacy Protection Act (applies to sites targeting kids under 13)
- HIPAA: Health Insurance Portability and Accountability Act (healthcare data)
- GLBA: Gramm-Leach-Bliley Act (financial data)
- FTC Act Section 5: Gives the FTC authority to pursue "unfair or deceptive" practices, including privacy violations
For most websites, federal law won't require a cookie banner. But state laws? That's a different story.
State laws: a growing list
Multiple US states have enacted privacy laws, each with slightly different requirements:
California (CCPA/CPRA, 2020/2023): The California Consumer Privacy Act, enhanced by the California Privacy Rights Act, is the most comprehensive US privacy law. It requires:
- Clear privacy notices explaining what data you collect and why
- A "Do Not Sell or Share My Personal Information" link
- The ability for users to opt out of data selling/sharing
- The ability for users to request access, deletion, and correction of their data
Importantly, CCPA does NOT require opt-in consent for cookies. It's an opt-out model. You can track by default, but you must provide an easy opt-out mechanism.
Other states with privacy laws:
- Virginia (VCDPA): effective January 2023
- Colorado (CPA): effective July 2023
- Connecticut (CTDPA): effective July 2023
- Utah (UCPA): effective December 2023
- Texas, Oregon, Montana, Delaware: already in force by the time we wrote this (Texas and Oregon in July 2024, Montana in October 2024, Delaware in January 2025), and more states have followed
Most of these follow an opt-out model similar to CCPA rather than GDPR's opt-in approach.
Recent Development: States are increasingly scrutinising cookie banner UI design. The new Consortium of Privacy Regulators is coordinating enforcement of cookie banner implementation across multiple states, targeting "dark patterns" (nudging users to accept). Example: California's CPPA criticised banners that let users accept with one click but make rejecting require multiple clicks (asymmetrical choice).
Real-world enforcement
Sephora (CCPA, 2022): Fined $1.2 million for failing to disclose that it was selling personal information and not processing opt-out requests. This was the first CCPA enforcement action.
Google and YouTube (FTC, 2019): Paid $170 million for COPPA violations related to collecting data on children without parental consent.
Meta/Facebook (Multiple, Ongoing): Has faced billions in fines across various US actions, mostly related to FTC consent decrees and deceptive practices.
Attorney General Actions: Multiple state AGs have filed actions against companies for privacy violations, even before their state privacy laws went into effect, using consumer protection statutes.
The stakes
US penalties vary by state:
- CCPA: Up to $7,500 per intentional violation (and $2,500 per unintentional violation), inflation-adjusted to $7,988 and $2,663 from January 2025
- Private Right of Action: Under CCPA, consumers can sue for data breaches (not just consent violations) for $100-$750 per consumer per incident (adjusted to $107-$799 from January 2025)
- Other State Laws: Similar penalty structures, typically $5,000-$7,500 per violation
- FTC Actions: Can result in multi-million dollar settlements
- Attorney General Lawsuits: Can be expensive to defend even if you win
- Consumer Lawsuits: Privacy class actions are increasing, targeting tracking and data practices
What Google requires
Here's where it gets interesting: Google does NOT require Consent Mode or consent signals for US traffic in the same way it does for EEA/UK traffic.
However:
- You still need to comply with applicable state privacy laws (which may require opt-out mechanisms)
- Many CMPs, including Enzuzo, show banners to US users anyway to demonstrate transparency and collect consent preferences
- Not having a consent mechanism makes it harder to comply with opt-out requests under CCPA and other state laws
- Ad platforms increasingly expect consent signals or compliance with regional laws
Risk level for non-compliance: LOW TO MEDIUM
You're unlikely to face immediate enforcement for cookie issues unless you're a large company or doing something particularly egregious. But the landscape is shifting, and more states are coming online with their own laws. Trends point to growing opt-in requirements even in the US.
The practical upshot: unless your audience is entirely U.S.-based and you're willing to bet on no one ever visiting from Europe or South Africa, you can't realistically skip consent banners. And if you're using Google Analytics or Ads, you can't even cheat: the platforms themselves demand the signals (for EEA, UK and Swiss visitors, anyway).
The illusion of data: what this actually means for analytics
It's tempting to think, "Fine, forget compliance, I'll just track everyone." But that creates a different problem: garbage data.
If you're tracking users who haven't consented, your metrics are technically illegal and ethically questionable. They're also unreliable, because many privacy-savvy users block scripts anyway. You might get more numbers, but they won't be more accurate.
That's the paradox: compliance kills data, but non-compliance doesn't save it either.
Analytics used to be the heartbeat of digital decision-making. Now it's a faint, irregular pulse that barely tells us whether the patient is alive. Every modern analytics dashboard is effectively a 3% sample pretending to represent the whole population. The rest? Modelled, estimated, or just gone.
Let's go back to our numbers and really break down what's happening:
The breakdown
- 2.75% Consent Accepted: We have full, legal, unambiguous permission to track these users with Google Analytics, set advertising cookies, do remarketing, etc. This is the gold standard.
- 0.63% Consent Rejected: These users explicitly said "no." We cannot track them with non-essential cookies. We respect that.
- 51.33% Ignored Banner: These users saw the banner but didn't interact with it. Legally, in GDPR/POPIA jurisdictions, this means no consent was given. We should NOT be tracking them with non-essential cookies. But are we? That depends on how our CMP is configured.
- 45.29% Banner Not Shown: These are likely return visitors who previously made a choice, or users with certain browser configurations, or bots. Their previous choice (if any) should be respected.
The analytics nightmare
With only 2.75% consent, our Analytics data is:
- Massively incomplete: Missing data on 97%+ of visitors
- Wildly inaccurate: Conversion rates, bounce rates, time on site, traffic sources: everything is skewed
- Statistically biased: The 2.75% who accept aren't a random sample. They may be more privacy-friendly, more engaged, or from certain geographies
- Useless for decision-making: You can't make confident business decisions based on data from 3% of your audience
- Modelling isn't helping enough: Google's Consent Mode v2 behavioural modelling tries to fill gaps, but it's still essentially guessing
Comparing to global benchmarks
Based on the research, here's how our numbers stack up:
Acceptance rate
- Milk Moon Studio: 2.75%
- Industry Average: 3-7% (EU), 10-20% (US), 5-10% (Global)
- What This Means: Slightly low but not unusual for strict opt-in
Rejection rate
- Milk Moon Studio: 0.63%
- Industry Average: Less than 1% (many users don't actively reject)
- What This Means: Normal: most users ignore rather than reject
Ignore rate
- Milk Moon Studio: 51.33%
- Industry Average: 40-60% industry-wide
- What This Means: Right in the middle: banner fatigue is real
Banner not shown
- Milk Moon Studio: 45.29%
- Industry Average: Varies by implementation
- What This Means: High: need to investigate why
Key insight: Our 2.75% acceptance isn't a failure. It's the new reality of privacy-first web analytics. Sites with really well-designed, trustworthy banners might hit 10-15% acceptance, but that's the ceiling. No one is getting 50% or 80% consent rates anymore (and if they are, their banner probably isn't actually compliant).
What this means for different scenarios
If you're running Google Ads:
- Remarketing lists shrink to ~3% of visitors
- Conversion tracking becomes unreliable
- Campaign optimisation suffers
- Ad spend efficiency drops
If you're only using Google Analytics (like us):
- Can't understand which content drives enquiries
- Can't see which traffic sources convert
- Can't optimise content strategy based on real behaviour
- Sample size too small for statistical significance
The bias problem: Users who accept cookies may be:
- More trusting of your brand
- More engaged with your content
- From specific demographics or regions
- Less privacy-conscious than average
This means your analytics aren't just incomplete, they're systematically biased toward a specific subset of your audience.
The risk maths: losing your data, or losing your case file?
So here's the million-dollar question: which is worse: losing your data, or losing your case file?
Is the data loss worse than the legal risk? Let's break down the scenarios:
Scenario A: remove the banner and track everyone
Pros:
- Full data on 100% of visitors (minus ad blockers)
- Accurate Analytics
- Effective advertising and remarketing
- Better business decisions based on complete data
- No more banner fatigue for users
- Could go from ~3% visibility to ~80% visibility (accounting for ad blockers)
Cons:
- Illegal under GDPR (for EU visitors): risk up to €20M or 4% of revenue
- Illegal under POPIA (for South African visitors): risk up to ZAR 10M
- Possibly illegal under US state laws (depending on implementation)
- Google won't cooperate (they require Consent Mode for the EEA, UK and Switzerland)
- Risk of fines ranging from thousands to millions
- Risk of being ordered to stop tracking entirely
- Reputational damage if caught
- Losing client trust (especially for agencies)
- Data becomes legally toxic: can't use it, have to delete it if ordered
- Any EU or SA visitor can file a complaint and trigger investigation
Scenario B: keep the banner and accept the data loss
Pros:
- Legal compliance with GDPR, POPIA, and US state laws
- No risk of fines for consent violations
- Ethical high ground (we respect user privacy)
- Client trust (we practise what we preach)
- Google cooperation (Consent Mode works properly)
- Data we do collect is legally sound
- Future-proof (regulations getting stricter, not looser)
Cons:
- 97%+ data loss on non-consenting users
- Inaccurate Analytics that can mislead business decisions
- Weak advertising performance due to limited audiences
- Competitive disadvantage if competitors track without consent (though they're taking legal risks)
- Can't make confident data-driven decisions
- Marketing ROI becomes unclear
Scenario C: geo-targeted approach
Pros:
- Legal compliance in jurisdictions that require it
- Better data from jurisdictions that don't require opt-in consent
- Balances risk and reward
- Could track 100% of US visitors, ~3% of EU/SA visitors
Cons:
- More complex setup (need accurate geolocation)
- Inconsistent user experience across regions
- Still lose data from EU and SA visitors
- Need to really understand where your visitors are coming from
- One misclassified EU visitor could still trigger GDPR investigation
Scenario D: optimise the banner to increase consent rates
Pros:
- Stay compliant while getting more consents
- Improve data quality without legal risk
- Better user experience (clearer, less annoying banners get higher acceptance)
- Might improve from 3% to 10-15% acceptance
Cons:
- Will never get to 100% consent (or even close)
- Takes time and testing to optimise
- Diminishing returns (even the best banners only hit 15-20% acceptance in strict opt-in mode)
- Risk of dark patterns if you push too hard for consent
The verdict
In a perfect world, we'd have complete data. But we don't live in that world anymore.
Skip the banner and track everyone:
You get clean data, but you're breaking GDPR and POPIA, risking multimillion-rand or euro fines, and you'll find Google's ecosystem quietly cutting you off.
Keep the banner and follow the law:
You lose 90-plus per cent of measurable behaviour but sleep better at night knowing you're not about to star in a regulator's press release.
It's a lose-lose scenario, just with different flavours of pain.
But this is what it comes down to: the cost of non-compliance (legal, fines, platform restrictions, reputational damage) outweighs the "benefit" of complete data that's legally toxic.
The data you collect via consent is legally robust and defensible. Illegal data is worthless data: you can't use it, and you may be forced to delete it anyway.
But there is a middle ground.
The pragmatic middle: geo-targeted and optimised
The only rational strategy right now is balance.
Show strict opt-in banners in the regions that demand them (the EU, UK, and South Africa) and relax to an opt-out model elsewhere. That recovers some data without courting disaster.
Then, optimise the banner itself:
- Clear language, not legalese
- Symmetrical buttons (accept and reject equally visible)
- A short explanation of why consent helps (trust still boosts acceptance)
- Minimal delay before showing, but not instantly on page load
- Don't nag users who've already made a choice
(Related: if all you need is a notice bar people can close, that doesn't need a cookie at all. We showed how in our post on a dismissible, session-based info banner in Webflow.)
Small tweaks can raise consent rates from 3% to 10%. Still terrible, but three times less terrible.
And if you can, invest in server-side analytics or privacy-friendly tools like Plausible or Fathom for broad, anonymous trends. They won't replace GA4 entirely, but they'll fill in some of the missing picture without triggering consent laws. If you're on Cloudflare, Zaraz is worth a look too: it runs your tags from Cloudflare's edge instead of the visitor's browser, and we walked through it in our guide to setting up Cloudflare Zaraz with GA4 on Webflow. It won't make the consent question go away, but it's a decent first step towards server-side.
What it means for us (and everyone like us)
Let's get specific about our situation. We're a small web design and development studio based in South Africa. We don't run ads. We don't need remarketing lists. We just want to know if anyone's actually reading our posts, and maybe understand which blog posts actually drive enquiries.
Would removing the banner fix that? Technically yes: we'd go from 3% visibility to maybe 80% (allowing for blockers).
But legally? That's a different story entirely.
Our specific situation
Location: South Africa (POPIA applies directly to us as the data controller)
Audience: Mix of USA (majority), South Africa, and EU visitors
Tools: Google Analytics 4 (GA4) for website analytics
Advertising: None, right now. We're not running Google Ads, Facebook Ads, or any paid advertising with pixel tracking, but we turn it on and off and experiment.
Business Model: Service-based (web design/development agency)
Legal implications of removing the banner
POPIA risk (high, we're in South Africa)
This is the big one. We're a South African business, registered in South Africa, processing personal information of data subjects. POPIA applies to us directly and unambiguously.
If we remove the consent banner and track SA visitors without consent:
- We're directly violating POPIA's consent requirements
- We're processing personal information (IP addresses, device IDs, browsing behaviour) without lawful justification
- We're exposed to fines up to ZAR 10 million
- We're exposed to potential criminal liability (yes, jail time, if it ever got as far as ignoring an enforcement notice)
Realistic enforcement probability:
The Information Regulator is still ramping up enforcement, and they're prioritising egregious cases (big data breaches, malicious actors, complaints about marketing spam). Would they come after a small web agency for running Analytics without consent?
Probably not immediately. But:
- Any SA visitor can file a complaint against us
- We can't hide: we're a registered business with a public website
- The risk compounds over time: the longer we operate non-compliantly, the more exposure we have
- The penalties are severe: even ZAR 1 million would be devastating; ZAR 10 million would be business-ending
- Ignoring an enforcement notice can mean criminal prosecution, and personal liability for the people responsible
We could argue enforcement is slow, that regulators chase big fish, that no one cares about one small Webflow agency in the Overberg, but that's not the point. The point is: the law exists, and ignoring it while advising clients on compliance would be a spectacular own goal.
Our assessment: This is not a risk we can justify. Even if probability is low, severity is catastrophic. In risk management terms: Low probability × Catastrophic impact = Don't do it.
GDPR risk (medium, we have EU visitors)
We're not based in the EU, but we have EU visitors. If we're offering services to EU data subjects (which we are: our website is publicly accessible and we accept EU clients), GDPR applies to us under its territorial scope provisions.
If we remove the consent banner and track EU visitors without consent:
- We're violating GDPR for any EU visitors to our site
- We're exposed to fines up to €20 million or 4% of global revenue
- Any EU visitor can file a complaint with their national DPA
- EU DPAs can (and do) pursue non-EU businesses under GDPR's territorial scope
Our assessment: Meaningful risk, especially if we grow or if a single EU visitor decides to file a complaint.
USA risk (low, but not zero)
For our US visitors, the risk is much lower. No federal cookie consent law, and state laws use opt-out models, not opt-in. We could potentially track US visitors without a banner and just provide an opt-out mechanism.
Our assessment: The US portion of our traffic could legally be tracked without upfront consent, as long as we provide opt-out mechanisms.
Data quality implications
Current state (with consent banner):
- 2.75% consent acceptance rate
- Tracking 2.75% of visitors with full functionality
- 97%+ data loss
- Severely incomplete Analytics data
- Can't make confident decisions based on data
If we removed the banner:
- 100% tracking (for visitors without ad blockers, ~75-85% of users)
- Complete view of user behaviour
- Accurate metrics on traffic sources, user journeys, conversion paths, content performance
- The data improvement would be massive: from ~3% visibility to ~80% visibility
With complete data, we could:
- Understand which blog posts actually drive enquiries (currently guessing)
- See which traffic sources convert best (sample size too small now)
- Optimise our content strategy based on real behaviour
- Make better decisions about where to invest time
- Track actual ROI on content marketing efforts
This is not trivial. For a small business, having accurate data vs. 97% data loss is the difference between flying blind and making informed decisions.
The Google Analytics factor (without advertising)
Here's where our situation differs: We're not running Google Ads. (Sometimes we are)
This changes the equation because:
- Google's Consent Mode requirement is less critical for us. The main pressure from Google is around advertising products. GA4 will still collect data without Consent Mode. We'll just be doing so non-compliantly in GDPR/POPIA jurisdictions.
- We don't lose advertising functionality. Many businesses can't remove the banner because Google Ads won't work properly. We don't have that constraint.
- GA4 will function. Google Analytics 4 doesn't stop working if you don't have a consent banner. It just collects data that may be legally problematic.
So from a pure "will the tools work?" perspective, yes, GA4 would work fine without the banner.
But that doesn't make it legal.
The ethical and reputational dimension
There's another factor: We're a web agency.
If we remove our consent banner:
- What do we tell clients? Advise them to use banners while we don't? That's hypocritical.
- What if clients discover we're non-compliant? Why would they trust us to build compliant sites?
- What message does it send? "We know the law but choose to ignore it" isn't great for a professional services firm.
- Reputational risk: If we get caught or fined, that's public. In South Africa's small web dev community, that news spreads.
This isn't just legal or data. It's business credibility.
The final verdict: what should Milk Moon Studio do?
After analysing everything, here's our conclusion:
We cannot justify removing the consent banner, despite the massive data loss.
Here's why:
1. POPIA risk is too high
We're a South African business. POPIA applies directly. The penalties (a ZAR 10 million fine, and jail if an enforcement notice is ignored) are severe. Enforcement is increasing. This alone makes removing the banner unjustifiable.
Even if the probability of enforcement is relatively low right now, the severity of the outcome is business-ending. Low probability × Catastrophic impact = Don't do it.
2. GDPR risk compounds the problem
Adding EU visitors into the mix makes the legal risk even worse. We'd be non-compliant in two major jurisdictions, both with severe penalties.
3. The data gain doesn't outweigh the legal risk
Yes, we'd get much better data. But:
- We can't make business decisions if we're facing a ZAR 10 million fine
- We can't optimise content while defending against an Information Regulator investigation
- Better Analytics data is worthless if it costs us our business
4. We're a professional services firm
We advise clients on web best practices. We can't be non-compliant ourselves. The reputational risk is too high.
5. The industry is moving toward privacy, not away from it
POPIA enforcement will get stricter, not looser. More countries are implementing privacy laws. The trend is toward more regulation, not less. Being non-compliant now means we're on the wrong side of where things are heading.
What we're actually going to do
Given all of this, here's our plan:
1. Keep the consent banner (non-negotiable for POPIA and GDPR compliance)
2. Implement geo-targeting:
- Strict opt-in for SA and EU visitors (required by law)
- Opt-out model for US visitors (allowed under US law, improves data collection)
3. Optimise the banner to improve acceptance rates:
- Test different messaging
- Make the value proposition clearer
- Simplify the UI
- Make rejection as easy as acceptance (counterintuitively, this can increase acceptance by building trust)
- Try different banner designs and placements
4. Accept the data loss from non-consenting users as a cost of legal operation
5. Use the data we do have more intelligently:
- Focus on trends rather than absolute numbers
- Use qualitative feedback to supplement quantitative data
- Accept that 3% accurate data is better than 100% illegal data
- Segment "consented" vs "non-consented (modelled)" in reports
6. Explore privacy-friendly alternatives:
- Consider server-side analytics that don't require cookie consent
- Look into first-party data collection methods
- Investigate analytics tools that don't process personal data (like Plausible, Fathom)
The bottom line for Milk Moon Studio
The 97% data loss hurts. It makes our Analytics nearly useless. It's frustrating.
But the legal risk of operating without consent in South Africa is not acceptable. We'd be processing personal data without consent under POPIA, which carries up to ZAR 10 million in fines, and jail if an enforcement notice is ignored. That's not a risk we can justify to ourselves, our clients, or our accountants.
Add in the GDPR risk for EU visitors, the reputational risk as a web agency, and the ethical dimension of practising what we preach, and the answer is clear.
We're keeping the consent banner, optimising it where we can, and accepting the data loss as a cost of legal and ethical business operations.
So we're keeping the banner. We'll geo-target it, refine it, and accept that our analytics are a polite fiction.
It's not the answer we wanted. But it's the right answer.
The new normal: what this means for the web
Let's zoom out for a moment. What we're experiencing isn't unique to Milk Moon Studio. It's happening across the entire web.
The uncomfortable truth is that the age of perfect analytics is over.
Consent banners didn't just limit tracking; they changed what "data-driven" means. For years, we've operated under the assumption that you could track everyone who visited your website. That era is over. The new reality is:
- Most users don't consent to tracking (3-10% acceptance rates globally)
- Most users ignore cookie banners (40-60% never interact)
- The data we collect is systematically biased (consenting users aren't a random sample)
- Google's modelling tries to compensate (but it's guessing, not measuring)
- Legal enforcement is increasing (billions in fines, active investigations)
- Platform requirements are tightening (Google mandating Consent Mode v2)
This is the new normal.
Web professionals need to adjust expectations:
- Analytics will always be incomplete
- Conversion tracking will always be fuzzy
- Ad remarketing will always be limited
- Business decisions will require more qualitative input
- Sample sizes will always be smaller than we'd like
The question isn't "How do we get back to 100% tracking?" (Answer: You don't, legally.)
The question is "How do we make good business decisions with 3-10% tracking data supplemented by modelling and qualitative insights?"
Decisions now have to rely on smaller, cleaner datasets, qualitative research, and (shockingly) actual human judgment.
That's not a bad thing. It's just different.
For agencies and marketers, this shift forces a return to fundamentals: compelling content, real engagement, and trust. Because in a world where only 3% of users say "yes," the ones who do are the ones who actually care.
Recommendations for different scenarios
If you have ANY EU or South African visitors:
You need a consent banner. Full stop. The legal risk is too high, and for your EU, UK and Swiss visitors Google won't work properly without it.
Recommended tools for Webflow:
- Enzuzo (what we use, integrates well with Webflow)
- CookieYes
- Cookiebot
- Osano
- Termly
All of these integrate with Webflow and support Google Consent Mode v2. We'd wire the Consent Mode side up through Google Tag Manager, and here's the general case for using it in Webflow: our post on why you should use Google Tag Manager in Webflow. If you haven't got Tag Manager on the site yet, start with our guide to adding Google Tag Manager and Google Analytics to Webflow.
If you're US-only:
You have more flexibility:
- Option A: Implement a consent banner anyway (best practice, builds trust, future-proofs against new state laws)
- Option B: Use a minimal notice with an opt-out link (CCPA compliance)
- Option C: No banner, but have a clear privacy policy and opt-out mechanism somewhere on your site
Be honest with yourself about whether you're truly US-only. Check your Analytics. If you see EU or SA traffic, you need the banner.
For Webflow designers/agencies:
This is a client education opportunity. Many clients don't understand:
- What cookie consent is or why it matters
- That the law applies to them
- That Google requires it for proper functionality (for EU, UK and Swiss visitors)
- That everyone is dealing with data loss, not just them
Set proper expectations:
- "Your Analytics data will be incomplete, and that's normal and legal."
- "We're tracking the users who matter most: the ones who trust you enough to consent."
- "Not having a consent banner exposes you to fines that could end your business."
Best practices for optimising your banner (and your cookie consent rate)
Since you're stuck with the banner, make it work better:
- Keep it simple: Don't overwhelm users with options
- Be transparent: Explain what you're collecting and why
- Make rejection easy: Builds trust, may paradoxically increase acceptance
- Test different designs: A/B test banner styles, copy, placement, timing
- Use geo-targeting: Show different banners to different regions based on legal requirements
- Support Consent Mode v2: Let Google model data for non-consenters
- Document everything: Keep records of consent for compliance audits
- Avoid dark patterns: Don't make "Accept" easy and "Reject" buried (regulators are watching)
- Monitor and iterate: Track your consent rates and continuously improve
Reducing "Banner Not Shown"
If 45% of your users never see the banner (like ours), investigate:
- Geolocation logic (are you excluding too many regions?)
- Return visitor logic (are cookies persisting properly?)
- Script errors (is the banner failing to load?)
- Bot traffic (are bots being counted?)
- Browser compatibility (does it work on all browsers?)
FAQ
What is a normal cookie consent rate?
It depends a lot on what you divide by. Enzuzo gave us a 2.75% cookie consent rate, but that's measured against every pageview, including the 45% where the banner never showed. Count only the pageviews where it did show and we're closer to 5%. Studies that look at people who actually get the banner land a lot higher: Advance Metrics followed up its 2018 study of more than 1.2 million users by looking at international B2B websites in the first half of 2023, and found 25.4% accepted all cookies straight away, while 33.6% ignored the banner completely. So before you compare your number with anyone else's, check you're comparing the same thing.
What happens if my cookie consent banner isn't compliant with GDPR?
A regulator can order you to fix it and fine you. The cookie rules themselves come from each EU country's ePrivacy law (that's why France's CNIL fined Google €325 million in September 2025 under French cookie rules), while GDPR sets the standard for what counts as consent: no pre-ticked boxes, and saying no has to be as easy as saying yes. GDPR breaches can be fined up to €20 million or 4% of worldwide annual turnover, whichever is higher. On top of that, if you use Google Ads or Analytics for visitors in the EEA, UK or Switzerland, Google's own policy requires valid consent signals, and without them you lose remarketing and personalised ads for those visitors.
How likely is a small website to get fined for not having a cookie banner?
Low, but not zero, and it's rarely a fine out of the blue. Regulators spend most of their time on big players and serious breaches. What catches small sites is usually a complaint or a lawsuit. In Germany, a Munich court ordered a website operator to pay a visitor €100 in damages in January 2022 for loading Google Fonts without consent, and that ruling set off a wave of copycat warning letters to other site owners. In South Africa the route is a complaint or a breach, then an enforcement notice, then a fine if you ignore the notice, which is how the Department of Justice ended up with the first R5 million POPIA fine in 2023 (its route started with a breach).
Does POPIA require a cookie banner in South Africa?
POPIA has no cookie-specific rules. What it does say (section 11) is that you need a lawful ground to process personal information, and consent is one of six. Its definition of personal information includes online identifiers, so analytics and advertising cookies that tie browsing to a person count. That means you either get consent or you argue another ground, like legitimate interest. For analytics and marketing cookies we go with consent, which is why our banner stays.
Which analytics tools work without a cookie consent banner?
Cookieless, privacy-first tools like Plausible and Fathom are built for exactly this. Plausible, for example, doesn't set cookies or store IP addresses (it counts visitors with a hash that changes every day), which is why it says you don't need a consent banner for it. You get the broad trends (pageviews, referrers, top pages) without the 97% hole, but not the detailed user-level stuff GA4 gives you. Server-side tagging on its own doesn't get you out of consent: if you're still sending personal data to Google, you still need the yes.
Final thought: the seatbelt beep you can't ignore
Cookie consent banners are the digital equivalent of the seatbelt beep in your car: annoying, relentless, and impossible to ignore, but you still put the belt on because the alternative is worse.
Our 2.75% cookie consent rate is painful, and it's in line with global trends. Cookie consent banners are annoying. They kill data collection. They make advertising harder.
But here's the reality:
The legal risk of operating without proper consent in GDPR and POPIA jurisdictions is business-ending. A single GDPR fine could shut down a small agency or business. Ignoring the Information Regulator's enforcement notice in South Africa can end in jail.
Google won't cooperate without consent signals for EU, UK and Swiss visitors. Even if you're willing to gamble on enforcement, your tools won't work properly for that traffic. Google has essentially become the enforcement arm of GDPR.
Everyone else is dealing with the same data loss. Your competitors who have consent banners are seeing 3-10% acceptance rates too. The ones without banners are either US-only, uninformed, or taking massive legal risks.
Users actually appreciate transparency. Yes, consent rates are low. But the users who do consent are choosing to trust you. That's worth something.
The web analytics landscape has permanently changed. 100% tracking is no longer possible (legally). We're all learning to make business decisions with incomplete data supplemented by modelling and qualitative insights.
For Milk Moon Studio, we're keeping our consent banner. We're going to optimise it to improve our acceptance rate. We're going to geo-target it so US visitors get a less restrictive experience. And we're going to accept the data loss as the cost of doing business legally and ethically in 2025.
For anyone building websites in 2025: If you serve EU or South African visitors, you need a cookie consent solution. The legal risk isn't worth the data gain. And even if it were, Google won't let you collect that data effectively from EU, UK and Swiss visitors without consent signals anyway.
Our data may be smaller, our dashboards emptier, and our reports filled with caveats, but at least we're compliant, consistent, and credible.
So yes, we'll keep our banner. We'll optimise it, tweak it, maybe even A/B test the wording, but we're not pulling it down.
Because while 97% data loss stings, losing the right to operate stings a lot more.
---
Disclaimer: This post is not legal advice. We're a web design and development studio, not lawyers. For specific legal guidance on your situation, consult with a qualified attorney specialising in data protection and privacy law. Laws change, enforcement evolves, and your specific circumstances matter. This post reflects our understanding as of October 2025 and our decision-making process for our own business.